Privacy Policy
Privacy Policy Introduction and Overview
We have written this privacy policy (version 21.09.2026-113238923) in order to explain to you, in accordance with the provisions of the
General Data Protection Regulation (EU) 2016/679 and applicable national laws, which personal data (data for short) we as the controller – and the processors commissioned by us (e.g. providers) – process, will process in the future and what legal options you have. The terms used are to be considered gender-neutral.
In short: We provide you with comprehensive information about any of your personal data we process.
Privacy policies usually sound very technical and use legal terminology. However, this privacy policy is intended to describe the most important things to you as simply and transparently as possible. So long as it aids transparency, technical
terms are explained in a reader-friendly manner, links to further information are provided and
graphics are used. We are thus informing in clear and simple language that we only process personal data in the context of our business activities if there is a legal basis for it. This is certainly not possible with brief, unclear and legal-technical statements, as is often standard on the internet when it comes to data protection. I hope you find the following explanations interesting and informative. Maybe you will also find some information that you have not been familiar with.
If you still have questions, we kindly ask you to contact the responsible body named below or in the imprint, follow the existing links and look at further information on third-party sites. You can of course also find our contact details in the imprint.
Scope
This privacy policy applies to all personal data processed by our company and to all personal data processed by companies commissioned by us (processors). With the term personal data, we refer to information within the meaning of Article 4 No. 1 GDPR, such as the name, email address and postal address of a person. The processing of personal data ensures that we can offer and invoice our services and products, be it online or offline. The scope of this privacy policy includes:
- all online presences (websites, online shops) that we operate
- Social media presences and email communication
- mobile apps for smartphones and other devices
In short: This privacy policy applies to all areas in which personal data is processed in a structured manner by the company via the channels mentioned. Should we enter into legal relations with you outside of these channels, we will inform you separately if necessary.
Legal bases
In the following privacy policy, we provide you with transparent information on the legal principles and regulations, i.e. the legal bases of the General Data Protection Regulation, which enable us to process personal data.
Whenever EU law is concerned, we refer to REGULATION (EU) 2016/679 OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of April 27, 2016. You can of course access the General Data Protection Regulation of the EU online at EUR-Lex, the gateway to EU law, at
https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=celex%3A32016R0679.
We only process your data if at least one of the following conditions applies:
- Consent (Article 6 Paragraph 1 lit. a GDPR): You have given us your consent to process data for a specific purpose. An example would be the storage of data you entered into a contact form.
- Contract (Article 6 Paragraph 1 lit. b GDPR): We process your data in order to fulfill a contract or pre-contractual obligations with you. For example, if we conclude a sales contract with you, we need personal information in advance.
- Legal obligation (Article 6 Paragraph 1 lit. c GDPR): If we are subject to a legal obligation, we will process your data. For example, we are legally required to keep invoices for our bookkeeping. These usually contain personal data.
- Legitimate interests (Article 6 Paragraph 1 lit. f GDPR): In the case of legitimate interests that do not restrict your basic rights, we reserve the right to process personal data. For example, we have to process certain data in order to be able to operate our website securely and economically. Therefore, the processing is a legitimate interest.
Other conditions such as making recordings in the interest of the public, the exercise of official authority as well as the protection of vital interests do not usually occur with us. Should such a legal basis be relevant, it will be disclosed in the appropriate place.
In addition to the EU regulation, national laws also apply:
- In Austria this is the Austrian Data Protection Act (Datenschutzgesetz), in short DSG.
- In Germany this is the Federal Data Protection Act (Bundesdatenschutzgesetz), in short BDSG.
Should other regional or national laws apply, we will inform you about them in the following sections.
Contact details of the data protection controller
If you have any questions about data protection or the processing of personal data, you will find below the contact details of the controller in accordance with Article 4(7) of the EU General Data Protection Regulation (GDPR):
Auxiliaris Steuerberatung GmbH
Nikolaiplatz 9
8480 Mureck
E-Mail:
steuerberatung@auxiliaris.at
Phone:
+43 (0) 3472 2549
Company details:
https://steuerberatung-auxiliaris.com/impressum-auxiliaris-steuerberatung/
Storage Period
It is a general criterion for us to store personal data only for as long as is absolutely necessary for the provision of our services and products. This means that we delete personal data as soon as any reason for the data processing no longer exists. In some cases, we are legally obliged to keep certain data stored even after the original purpose no longer exists, such as for accounting purposes.
If you want your data to be deleted or if you want to revoke your consent to data processing, the data will be deleted as soon as possible, provided there is no obligation to continue its storage.
We will inform you below about the specific duration of the respective data processing, provided we have further information.
Rights in accordance with the General Data Protection Regulation
In accordance with Articles 13, 14 of the GDPR, we inform you about the following rights you have to ensure fair and transparent processing of data:
- According to Article 15 DSGVO, you have the right to information about whether we are processing data about you. If this is the case, you have the right to receive a copy of the data and to know the following information:
- for what purpose we are processing;
- the categories, i.e. the types of data that are processed;
- who receives this data and if the data is transferred to third countries, how security can be guaranteed;
- how long the data will be stored;
- the existence of the right to rectification, erasure or restriction of processing and the right to object to processing;
- that you can lodge a complaint with a supervisory authority (links to these authorities can be found below);
- the origin of the data if we have not collected it from you;
- Whether profiling is carried out, i.e. whether data is automatically evaluated to arrive at a personal profile of you.
- You have a right to rectification of data according to Article 16 GDPR, which means that we must correct data if you find errors.
- You have the right to erasure (“right to be forgotten”) according to Article 17 GDPR, which specifically means that you may request the deletion of your data.
- According to Article 18 of the GDPR, you have the right to restriction of processing, which means that we may only store the data but not use it further.
- According to Article 20 of the GDPR, you have the right to data portability, which means that we will provide you with your data in a standard format upon request.
- According to Article 21 DSGVO, you have the right to object, which entails a change in processing after enforcement.
- If the processing of your data is based on Article 6(1)(e) (public interest, exercise of official authority) or Article 6(1)(f) (legitimate interest), you may object to the processing. We will then check as soon as possible whether we can legally comply with this objection.
- If data is used to conduct direct advertising, you may object to this type of data processing at any time. We may then no longer use your data for direct marketing.
- If data is used to conduct profiling, you may object to this type of data processing at any time. We may no longer use your data for profiling thereafter.
- According to Article 22 of the GDPR, you may have the right not to be subject to a decision based solely on automated processing (for example, profiling).
- You have the right to lodge a complaint under Article 77 of the GDPR. This means that you can complain to the data protection authority at any time if you believe that the data processing of personal data violates the GDPR.
In short: you have rights – do not hesitate to contact the responsible party listed above with us!
If you believe that the processing of your data violates data protection law or your data protection rights have been violated in any other way, you can complain to the supervisory authority. For Austria, this is the data protection authority, whose website can be found at
https://www.dsb.gv.at/. In Germany, there is a data protection officer for each federal state. For more information, you can contact the Federal Commissioner for
Data Protection and Freedom of Information (BfDI). The following local data protection authority is responsible for our company:
Data transfer to third countries
We only transfer or process data to countries outside the scope of the GDPR (third countries) if you consent to this processing or if there is another legal permission. This is particularly true when processing is legally required or necessary for the performance of a contractual relationship, and in any case, only to the extent permitted by law. Your consent is in most cases the primary reason for us to process data in third countries. Processing of personal data in third countries such as the USA, where many software providers offer services and have their server locations, may mean that personal data is processed and stored in unexpected ways.
We explicitly point out that, according to the opinion of the European Court of Justice, there is currently only an adequate level of protection for data transfers to the USA if a US company processing personal data of EU citizens in the USA is an active participant in the EU-US Data Privacy Framework. More information can be found at:
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en
Data processing by US services that are not active participants in the EU-US Data Privacy Framework may result in data not being anonymized and processed, if applicable. Additionally, US government authorities may potentially have access to individual data. Furthermore, it may occur that collected data is linked with data from other services of the same provider, if you have a corresponding user account. Where possible, we try to use server locations within the EU, if offered.
We will inform you in the appropriate sections of this privacy policy in more detail about data transfers to third countries, if applicable.
Security of data processing operations
In order to protect personal data, we have implemented both technical and organisational measures. We encrypt or pseudonymise personal data wherever this is possible. Thus, we make it as difficult as we can for third parties to extract personal information from our data.
Article 25 of the GDPR refers to “data protection by technical design and by data protection-friendly default” which means that both software (e.g. forms) and hardware (e.g. access to server rooms) appropriate safeguards and security measures shall always be placed. If applicable, we will outline the specific measures below.
TLS encryption with https
The terms TLS, encryption and https sound very technical, which they are indeed. We use HTTPS (Hypertext Transfer Protocol Secure) to securely transfer data on the Internet.
This means that the entire transmission of all data from your browser to our web server is secured – nobody can “listen in”.
We have thus introduced an additional layer of security and meet privacy requirements through technology design
Article 25 Section 1 GDPR). With the use of TLS (Transport Layer Security), which is an encryption protocol for safe data transfer on the internet, we can ensure the protection of confidential information.
You can recognise the use of this safeguarding tool by the little lock-symbol

, which is situated in your browser’s top left corner in the left of the internet address (e.g. examplepage.uk), as well as by the display of the letters https (instead of http) as a part of our web address.
If you want to know more about encryption, we recommend you to do a Google search for “Hypertext Transfer Protocol Secure wiki” to find good links to further information.
Communications
| Communications Overview
👥 Affected parties: Anyone who communicates with us via phone, email or online form
🤝 Processed data: e. g. telephone number, name, email address or data entered in forms. You can find more details on this under the respective form of contact
📓 Purpose: handling communication with customers, business partners, etc.
📅 Storage duration: for the duration of the business case and the legal requirements
⚖️ Legal basis: Article 6 (1) (a) GDPR (consent), Article 6 (1) (b) GDPR (contract), Article 6 (1) (f) GDPR (legitimate interests) |
If you contact us and communicate with us via phone, email or online form, your personal data may be processed.
The data will be processed for handling and processing your request and for the related business transaction. The data is stored for this period of time or for as long as is legally required.
Affected persons
The above-mentioned processes affect all those who seek contact with us via the communication channels we provide.
Telephone
When you call us, the call data is stored in a pseudonymised form on the respective terminal device, as well as by the telecommunications provider that is being used. In addition, data such as your name and telephone number may be sent via email and stored for answering your inquiries. The data will be erased as soon as the business case has ended and the legal requirements allow for its erasure.
Email
If you communicate with us via email, your data is stored on the respective terminal device (computer, laptop, smartphone, …) as well as on the email server. The data will be deleted as soon as the business case has ended and the legal requirements allow for its erasure.
Online forms
If you communicate with us using an online form, your data is stored on our web server and, if necessary, forwarded to our email address. The data will be erased as soon as the business case has ended and the legal requirements allow for its erasure.
Legal bases
Data processing is based on the following legal bases:
- Art. 6 para. 1 lit. a GDPR (consent): You give us your consent to store your data and to continue to use it for the purposes of the business case;
- Art. 6 para. 1 lit. b GDPR (contract): For the performance of a contract with you or a processor such as a telephone provider, or if we have to process the data for pre-contractual activities, such as preparing an offer;
- Art. 6 para. 1 lit. f GDPR (legitimate interests): We want to conduct our customer inquiries and business communication in a professional manner. Thus, certain technical facilities such email programs, Exchange servers and mobile network operators are necessary to efficiently operate our communications.
Cookies
| Cookies Overview
👥 Affected parties: visitors to the website
🤝 Purpose: depending on the respective cookie. You can find out more details below or from the software manufacturer that sets the cookie.
📓 Processed data: depends on the cookie used. More details can be found below or from the manufacturer of the software that sets the cookie.
📅 Storage duration: can vary from hours to years, depending on the respective cookie
⚖️ Legal basis: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What are cookies?
Our website uses HTTP-cookies to store user-specific data.
In the following we explain what cookies are and why they are used, so that you can better understand the following privacy policy.
Whenever you surf the Internet, you are using a browser. Common browsers are for example, Chrome, Safari, Firefox, Internet Explorer and Microsoft Edge. Most websites store small text-files in your browser. These files are called cookies.
It is important to note that cookies are very useful little helpers. Almost every website uses cookies. More precisely, these are HTTP cookies, as there are also other cookies for other uses. HTTP cookies are small files that our website stores on your computer. These cookie files are automatically placed into the cookie-folder, which is the “brain” of your browser. A cookie consists of a name and a value. Moreover, to define a cookie, one or multiple attributes must be specified.
Cookies store certain user data about you, such as language or personal page settings. When you re-open our website to visit again, your browser submits these “user-related” information back to our site. Thanks to cookies, our website knows who you are and offers you the settings you are familiar to. In some browsers, each cookie has its own file, while in others, such as Firefox, all cookies are stored in one single file.
The following graphic shows a possible interaction between a web browser such as Chrome and the web server. The web browser requests a website and receives a cookie back from the server. The browser then uses this again as soon as another page is requested.

There are both first-party cookies and third-party cookies. First-party cookies are created directly by our site, while third-party cookies are created by partner-websites (e.g. Google Analytics). Each cookie must be evaluated individually, as each cookie stores different data. The expiry time of a cookie also varies from a few minutes to a few years. Cookies are not software programs and do not contain viruses, trojans or other malware. Cookies also cannot access your PC’s information.
This is an example of how cookie-files can look:
Name: _ga
Value: GA1.2.1326744211.152113238923-9
Purpose: Differentiation between website visitors
Expiry date: after 2 years
A browser should support these minimum sizes:
- At least 4096 bytes per cookie
- At least 50 cookies per domain
- At least 3000 cookies in total
Which types of cookies are there?
The exact cookies that we use, depend on the used services, which will be outlined in the following sections of this privacy policy. Firstly, we will briefly focus on the different types of HTTP-cookies.
There are 4 different types of cookies:
Essential cookies
These cookies are necessary to ensure the basic functions of a website. They are needed when a user for example puts a product into their shopping cart, then continues surfing on different websites and comes back later in order to proceed to the checkout. These cookies ensure the shopping cart does not get deleted, even if the user closes their browser window.
Purposive cookies
These cookies collect information about user behaviour and whether the user receives any error messages. Furthermore, these cookies record the website’s loading time as well as its behaviour in different browsers.
Target-orientated cookies
These cookies ensure better user-friendliness. Thus, information such as previously entered locations, fonts sizes or data in forms stay stored.
Advertising cookies
These cookies are also known as targeting cookies. They serve the purpose of delivering customised advertisements to the user. This can be very practical, but also rather annoying.
Upon your first visit to a website you are usually asked which of these cookie-types you want to accept. Furthermore, this decision will of course also be stored in a cookie.
If you want to learn more about cookies and do not mind technical documentation, we recommend
https://tools.ietf.org/html/rfc6265, the Request for Comments of the Internet Engineering Task Force (IETF) called “HTTP State Management Mechanism”.
Purpose of processing via cookies
The purpose ultimately depends on the respective cookie. You can find out more details below or from the software manufacturer that sets the cookie.
Which data are processed?
Cookies are little helpers for a wide variety of tasks. Unfortunately, it is not possible to tell which data is generally stored in cookies, but in the privacy policy below we will inform you on what data is processed or stored.
Storage period of cookies
The storage period depends on the respective cookie and is further specified below. Some cookies are erased after less than an hour, while others can remain on a computer for several years.
You can also influence the storage duration yourself. You can manually erase all cookies at any time in your browser (also see “Right of objection” below). Furthermore, the latest instance cookies based on consent will be erased is after you withdraw your consent. The legality of storage will remain unaffected until then.
Right of objection – how can I erase cookies?
You can decide for yourself how and whether you want to use cookies. Regardless of which service or website the cookies originate from, you always have the option of erasing, deactivating or only partially accepting cookies. You can for example block third-party cookies but allow all other cookies.
If you want to find out which cookies have been stored in your browser, or if you want to change or erase cookie settings, you can find this option in your browser settings:
Chrome: Clear, enable and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies and site data in Firefox
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete cookies in Microsoft Edge
If you generally do not want cookies, you can set up your browser in a way to notify you whenever a cookie is about to be set. This gives you the opportunity to manually decide to either permit or deny the placement of every single cookie. This procedure varies depending on the browser. Therefore, it might be best for you to search for the instructions in Google. If you are using Chrome, you could for example put the search term “delete cookies Chrome” or “deactivate cookies Chrome” into Google.
Legal basis
The so-called “cookie directive” has existed since 2009. It states that the storage of cookies requires your
consent (Article 6 Paragraph 1 lit. a GDPR). Within countries of the EU, however, the reactions to these guidelines still vary greatly. In Austria, however, this directive was implemented in Section 165 (3) of the Telecommunications Act (2021). In Germany, the cookie guidelines have not been implemented as national law. Instead, this guideline was largely implemented in Section 15 (3) of the Telemedia Act (TMG), which has been replaced by the Digital Services Act (DSA) since May 2024.
For absolutely necessary cookies, even if no consent has been given, there are legitimate interests (Article 6 (1) (f) GDPR), which in most cases are of an economic nature. We want to offer our visitors a pleasant user experience on our website. For this, certain cookies often are absolutely necessary.
This is exclusively done with your consent, unless absolutely necessary cookies are used. The legal basis for this is Article 6 (1) (a) of the GDPR.
In the following sections you will find more detail on the use of cookies, provided the used software does use cookies.
Application Data
| Application Data Summary
👥 Affected Parties: Users applying for a job position with us
🤝 Purpose: Processing a job application procedure
📓 Processed Data: Name, address, contact details, email address, phone number, proof of qualifications (certificates), potentially data of special categories.
📅 Retention Period: For successful applications, data will be retained until the end of the employment relationship. Otherwise, the data will be deleted after the application process or stored for a certain period with your consent.
⚖️ Legal Basis: Art. 6(1)(a) GDPR (consent), legitimate interest (Art. 6(1)(f) GDPR), Art. 6(1)(b) GDPR (contract), Art. 9(2)(a) GDPR (processing special categories of data) |
What is application data?
You can apply for a job at our company via email, online form, or a recruiting tool. All data we receive and process as part of an application is considered application data. This includes personal data such as name, date of birth, address, and phone number.
Why do we process application data?
We process your data to carry out a proper selection process for the advertised position. Additionally, we may retain your application documents in our applicant archive. Often, we are impressed by a candidate and their application but cannot proceed with collaboration for various reasons. With your consent, we archive your documents so we can easily contact you for future opportunities in our company.
We assure you that we handle your data with the utmost care and always process it within the legal framework. Within our company, your data is only shared with individuals directly involved in your application process. In short: Your data is safe with us!
What data is processed?
For example, when you apply via email, we naturally receive personal data as mentioned above. Even the email address itself is considered personal data. During the application process, only data relevant to deciding whether we would like to welcome you to our team is processed.
The specific data processed depends primarily on the job listing. However, it usually includes your name, date of birth, contact details, and proof of qualifications. If you submit your application via an online form, the data is transmitted to us in encrypted form. If you send your application via email, this encryption does not occur, and we cannot take responsibility for the transmission method. Once the data is on our servers, we are responsible for its lawful handling.
During the application process, information about your health or ethnic origin may also be requested. This helps us comply with legal obligations related to labor law, social security, and social protection. These are considered special category data.
Here is a list of possible data we receive and process:
- Name
- Contact address
- Email address
- Phone number
- Date of birth
- Information from cover letters and resumes
- Proof of qualifications (e.g., certificates)
- Special category data (e.g., ethnic origin, health data, religious beliefs)
- Usage data (visited websites, access data, etc.)
- Metadata (IP address, device information)
How long is the data stored?
If you join our team, your data will be further processed for employment purposes and retained at least until the employment relationship ends. All application documents will then become part of your employee file.
If we do not offer you the position, you decline our offer, or withdraw your application, we may retain your data for up to 6 months after the application process ends under legitimate interest (Art. 6(1)(f) GDPR). After that, both electronic data and physical documents will be fully deleted or destroyed. We retain your data, for example, to answer follow-up questions or to provide evidence of the application in case of legal disputes. If a legal dispute arises and we need the data beyond the 6-month period, we will delete it only when there is no longer any reason to retain it. If there are statutory retention obligations, we must store the data longer than 6 months.
Furthermore, we may retain your data longer if you provide explicit consent. This might be the case if we see potential for future collaboration. In such cases, your data will be included in our applicant pool. Of course, you can withdraw your consent for extended retention at any time. If no withdrawal is made and no new consent is given, your data will be deleted after a maximum of 2 years.
Legal Basis
The legal bases for processing your data are Art. 6(1)(a) GDPR (consent), Art. 6(1)(b) GDPR (contract or pre-contractual measures), Art. 6(1)(f) GDPR (legitimate interests), and Art. 9(2)(a) GDPR (processing special categories of data).
If we include you in our applicant tool, it is based on your consent (Art. 6(1)(a) GDPR). We emphasize that your consent to join our applicant pool is voluntary, does not affect the application process, and can be withdrawn at any time. The legality of processing until the point of withdrawal remains unaffected.
In cases where vital interests are at stake, data processing occurs under Art. 9(2)(c) GDPR. For purposes related to healthcare, occupational medicine, medical diagnosis, provision of health or social care, or the management of systems and services in health or social care, data is processed under Art. 9(2)(h) GDPR. If you voluntarily provide special category data, processing is based on Art. 9(2)(a) GDPR.
| Contact Form Summary
👥 Data Subjects: Website visitors who enter data into a contact form
🤝 Purpose: Processing inquiries and communication in the context of pre-contractual measures or existing interest in our services
📓 Processed Data: Name, email address, phone number (if provided), message content, IP address, technical metadata (e.g., timestamp, browser information)
📅 Storage Duration: Data will be deleted as soon as it is no longer necessary for processing the inquiry and no legal retention obligations apply.
⚖️ Legal Bases: Consent (Art. 6 para. 1 lit. a GDPR), Legitimate Interest (Art. 6 para. 1 lit. f GDPR), Contract or pre-contractual measures (Art. 6 para. 1 lit. b GDPR) |
What is a contact form?
A contact form is a web form you can fill out on our website to get in touch with us easily. Typically, personal data such as your name, email address, and your message are transmitted to us. This information helps us respond to your inquiries more effectively and contact you directly.
Why do we use a contact form?
We offer a contact form to make it quick and easy for you to communicate with us. Whether you have questions about our services, want to give feedback, or have other concerns – the contact form allows you to reach out directly. The information you provide will be used solely to process your inquiry and to contact you. If the inquiry leads to further steps, such as providing an offer or entering into a contract, we may also use the data for those purposes.
What data is processed?
The specific data we process depends on the information you provide in the contact form. In general, this includes:
- Name
- Email address
- Phone number (optional)
- Message content
- Date and time of submission
- IP address and technical metadata (for security and traceability)
This information helps us understand and respond to your inquiry more efficiently.
How long is the data stored?
We store contact form data only as long as necessary to process your inquiry. If a business relationship arises, the same retention periods as for customer data apply. In certain cases (e.g., legal disputes), longer retention periods may be required. Of course, we do not share your data with third parties without your explicit consent.
Legal basis
The legal bases for processing your data via the contact form are Art. 6 para. 1 lit. a GDPR (consent – by submitting the form), Art. 6 para. 1 lit. b GDPR (pre-contractual measures), and Art. 6 para. 1 lit. f GDPR (legitimate interest – efficient communication and organization of inquiries). If you voluntarily provide special categories of personal data, processing is based on Art. 9 para. 2 lit. a GDPR (explicit consent).
Web hosting
| Web hosting Overview
👥 Affected parties: visitors to the website
📓 Purpose: professional hosting of the website and security of operations
🤝 Processed data: IP address, time of website visit, browser used and other data. You can find more details on this below or at the respective web hosting provider.
📅 Storage period: dependent on the respective provider, but usually 2 weeks
⚖️ Legal basis: Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is web hosting?
Every time you visit a website nowadays, certain information – including personal data – is automatically created and stored, including on this website. This data should be processed as sparingly as possible, and only with good reason. By website, we mean the entirety of all websites on your domain, i.e. everything from the homepage to the very last subpage (like this one here). By domain we mean example.uk or examplepage.com.
When you want to view a website on a screen, you use a program called a web browser. You probably know the names of some web browsers: Google Chrome, Microsoft Edge, Mozilla Firefox, and Apple Safari.
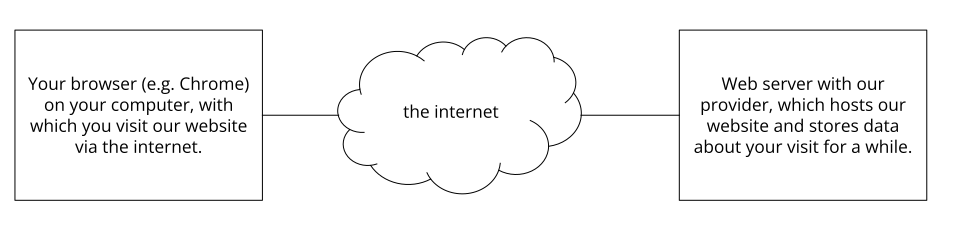
The web browser has to connect to another computer which stores the website’s code: the web server. Operating a web server is complicated and time-consuming, which is why this is usually done by professional providers. They offer web hosting and thus ensure the reliable and flawless storage of website data.
Whenever the browser on your computer establishes a connection (desktop, laptop, smartphone) and whenever data is being transferred to and from the web server, personal data may be processed. After all, your computer stores data, and the web server also has to retain the data for a period of time in order to ensure it can operate properly.
Illustration:
Why do we process personal data?
The purposes of data processing are:
- Professional hosting of the website and operational security
- To maintain the operational as well as IT security
- Anonymous evaluation of access patterns to improve our offer, and if necessary, for prosecution or the pursuit of claims.li>
Which data are processed?
Even while you are visiting our website, our web server, that is the computer on which this website is saved, usually automatically saves data such as
- the full address (URL) of the accessed website (e. g. https://www.examplepage.uk/examplesubpage.html?tid=113238923)
- browser and browser version (e.g. Chrome 87)
- the operating system used (e.g. Windows 10)
- the address (URL) of the previously visited page (referrer URL) (e. g. https://www.examplepage.uk/icamefromhere.html/)
- the host name and the IP address of the device from the website is being accessed from (e.g. COMPUTERNAME and 194.23.43.121)
- date and time
- in so-called web server log files
How long is the data stored?
Generally, the data mentioned above are stored for two weeks and are then automatically deleted. We do not pass these data on to others, but we cannot rule out the possibility that this data may be viewed by the authorities in the event of illegal conduct.
In short: Your visit is logged by our provider (company that runs our website on special computers (servers)), but we do not pass on your data without your consent!
Legal basis
The lawfulness of processing personal data in the context of web hosting is justified in Art. 6 para. 1 lit. f GDPR (safeguarding of legitimate interests), as the use of professional hosting with a provider is necessary to present the company in a safe and user-friendly manner on the internet, as well as to have the ability to track any attacks and claims, if necessary.
Hostinger Privacy Policy
We also use the webhosting service Hostinger for our business. The service provider is the Lithuanian company HOSTINGER, UAB, Švitrigailos Str. 34, LT-03230 Vilnius, Lithuania.
You can find out more about the data processed by using Hostinger in the privacy policy at
https://www.hostinger.co.uk/legal/privacy-policy.
Website Builders Introduction
| Website Builders Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: service optimisation
📓 Data processed: The data that is being processed includes but is not limited to technical usage information, browser activity, clickstream activity, session heat maps, contact details, IP addresses or geographic locations. You can find more details in the Privacy Policy below as well as in the providers’ Privacy Policies.
📅 Storage duration: depends on the provider
⚖️ Legal bases: Art. 6 (1) lit. f GDPR (legitimate interests), Art. 6 (1) lit. a GDPR (consent) |
What are website builders?
We use a modular website builder for our website. This is a special form of Content Management System (CMS). Website builders enable website operators to create websites very easily and without any programming knowledge. In many cases, web hosts also offer website builders. Your personal data may be collected, stored and processed if a website builder is being used. In this Privacy Policy, you will find general information about data that is processed by such modular website builder systems. You can find more information in the respective provider’s Privacy Policy.
Why do we use website builders for our website?
The greatest advantage of modular website builders is their ease of use. We want to offer you a clear, simple and nicely designed website that we can easily operate and maintain by ourselves – without needing any external support. Nowadays website builders offer many helpful functions that we can use even without having any programming knowledge. This enables us to design our website according to our wishes and therefore, to give you an informative and pleasant experience on our website.
Which data are stored by website builders?
First of all, the exact data that is stored depends on the website builder that is being used. Each provider processes and collects different data from website visitors. However, technical usage information such as users’ operating system, browser, screen resolution, language and keyboard settings, hosting provider as well as the date of the website visit are usually collected. Moreover, tracking data (e. g. browser activity, clickstream activities, session heat maps, etc.) may also be processed. The same goes for personal data, since data such as contact information e. g. email address, telephone number (if you have provided it), IP address and geographic location data may also be processed and stored. In the respective provider’s Privacy Policy you can find out exactly which of your data is getting stored.
How long and where are the data stored?
Provided that we have any further information on this, we will inform you below about the duration of the data processing associated with the website builder we use. You can find detailed information on this in the provider’s Privacy Policy. Generally, we only process personal data for as long as is absolutely necessary to provide our services and products. The provider may store your data according to their own specifications, over which we have no influence.
Right to object
You always retain the right to information, rectification and erasure of your personal data. If you have any questions, you can also contact the responsible parties at the respective website builder system at any time. You can find the corresponding contact details either in our Privacy Policy or on the website of the respective provider.
What is more, in your browser you can clear, disable or manage cookies that providers use for their functions. Depending on the browser you use, this can be done in different ways. Please note, that this may lead to not all functions working as usual anymore.
Legal Bases
We have a legitimate interest in using a website builder system to optimise our online service and present it in an efficient and user-friendly way. The corresponding legal basis for this is Article 6 (1) (f) GDPR (legitimate interests). However, we only use the website builder system if you have consented to it.
If the processing of data is not absolutely necessary for the operation of the website, your data will only be processed on the basis of your consent. This particularly applies to tracking activities. The legal basis for this is Article 6 (1) (a) GDPR.
With this Privacy Policy, we have made you more familiar with the most important general information on data processing. If you want to find out more about this, you will find further information – if available – in the following section or in the Privacy Policy of the provider.
Elementor Privacy Policy
We use the website builder system Elementor for our website. The service provider is the Israeli company Elementor Ltd., located at Rehov Tuval 40, 5252247 Ramat Gan, Israel.
Your data may be transferred to Israel. Israel is outside the scope of the General Data Protection Regulation (GDPR). However, the European Commission has decided, based on Article 45(1) of the GDPR, that Israel provides a level of protection comparable to the GDPR standards. You can view the decision here:
https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX%3A32011D0061
To learn more about the data processed through the use of Elementor, please refer to the privacy policy at
https://elementor.com/about/privacy/.
Web Analytics
| Web Analytics Privacy Policy Overview
👥 Affected parties: visitors to the website
🤝 Purpose: Evaluation of visitor information to optimise the website.
📓 Processed data: Access statistics that contain data such as access location, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. You can find more details on this from the respective web analytics tool directly.
📅 Storage period: depending on the respective web analytics tool used
⚖️ Legal basis: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is Web Analytics?
We use software on our website, which is known as web analytics, in order to evaluate website visitor behaviour. Thus, data is collected, which the analytic tool provider (also called tracking tool) stores, manages and processes. Analyses of user behaviour on our website are created with this data, which we as the website operator receive. Most tools also offer various testing options. These enable us, to for example test which offers or content our visitors prefer. For this, we may show you two different offers for a limited period of time. After the test (a so-called A/B test) we know which product or content our website visitors find more interesting. For such testing as well as for various other analyses, user profiles are created and the respective data is stored in cookies.
Why do we run Web Analytics?
We have a clear goal in mind when it comes to our website: we want to offer our industry’s best website on the market. Therefore, we want to give you both, the best and most interesting offer as well as comfort when you visit our website. With web analysis tools, we can observe the behaviour of our website visitors, and then improve our website accordingly for you and for us. For example, we can see the average age of our visitors, where they come from, the times our website gets visited the most, and which content or products are particularly popular. All this information helps us to optimise our website and adapt it to your needs, interests and wishes.
Which data are processed?
The exact data that is stored depends on the analysis tools that are being used. But generally, data such as the content you view on our website are stored, as well as e. g. which buttons or links you click, when you open a page, which browser you use, which device (PC, tablet, smartphone, etc.) you visit the website with, or which computer system you use. If you have agreed that location data may also be collected, this data may also be processed by the provider of the web analysis tool.
Moreover, your IP address is also stored. According to the General Data Protection Regulation (GDPR), IP addresses are personal data. However, your IP address is usually stored in a pseudonymised form (i.e. in an unrecognisable and abbreviated form). No directly linkable data such as your name, age, address or email address are stored for testing purposes, web analyses and web optimisations. If this data is collected, it is retained in a pseudonymised form. Therefore, it cannot be used to identify you as a person.
The following example shows Google Analytics’ functionality as an example for client-based web tracking with JavaScript code.

The storage period of the respective data always depends on the provider. Some cookies only retain data for a few minutes or until you leave the website, while other cookies can store data for several years.
Duration of data processing
If we have any further information on the duration of data processing, you will find it below. We generally only process personal data for as long as is absolutely necessary to provide products and services. The storage period may be extended if it is required by law, such as for accounting purposes for example for accounting.
Right to object
You also have the option and the right to revoke your consent to the use of cookies or third-party providers at any time. This works either via our cookie management tool or via other opt-out functions. For example, you can also prevent data processing by cookies by managing, deactivating or erasing cookies in your browser.
Legal basis
The use of Web Analytics requires your consent, which we obtained with our cookie popup. According to
Art. 6 para. 1 lit. a of the GDPR (consent), this consent represents the legal basis for the processing of personal data, such as by collection through Web Analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors, which enables us to technically and economically improve our offer. With Web Analytics, we can recognise website errors, identify attacks and improve profitability. The legal basis for this is
Art. 6 para. 1 lit. f of the GDPR (legitimate interests). Nevertheless, we only use these tools if you have given your consent.
Since Web Analytics tools use cookies, we recommend you to read our privacy policy on cookies. If you want to find out which of your data are stored and processed, you should read the privacy policies of the respective tools.
If available, information on special Web Analytics tools can be found in the following sections.
Google Analytics Privacy Policy
| Google Analytics Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: Evaluation of visitor information to optimise the website.
📓 Processed data: Access statistics that contain data such as the location of access, device data, access duration and time, navigation behaviour and click behaviour. You can find more details on this in the privacy policy below.
📅 Storage period: Customizable, GA4 stores data for 14 months by default.
⚖️ Legal basis: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is Google Analytics?
On our website, we use the analytics tracking tool Google Analytics in the Google Analytics 4 (GA4) version provided by the American company Google Inc. For the European region, Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. Google Analytics collects data about your actions on our website. By combining various technologies such as cookies, device IDs, and login information, you can be identified as a user across different devices. This allows your actions to be analyzed across platforms as well.
For example, when you click on a link, this event is stored in a cookie and sent to Google Analytics. With the reports we receive from Google Analytics, we can better tailor our website and service to your needs. In the following, we will provide more information about the tracking tool and specifically inform you about the data processed and how you can prevent it.
Google Analytics is a tracking tool used for website traffic analysis. The basis for these measurements and analyses is a pseudonymous user identification number. This number does not include personally identifiable information such as name or address but is used to assign events to a device. GA4 utilizes an event-based model that captures detailed information about user interactions such as page views, clicks, scrolling, and conversion events. Additionally, GA4 incorporates various machine learning features to better understand user behavior and certain trends. GA4 employs modeling through machine learning capabilities, meaning that based on the collected data, missing data can be extrapolated to optimize the analysis and provide forecasts.
In order for Google Analytics to function properly, a tracking code is embedded in the code of our website. When you visit our website, this code records various events that you perform on our website. With GA4’s event-based data model, we, as website operators, can define and track specific events to obtain analyses of user interactions. This allows us to track not only general information such as clicks or page views but also specific events that are important for our business, such as submitting a contact form or making a purchase.
Once you leave our website, this data is sent to and stored on Google Analytics servers.
Google processes the data, and we receive reports on your user behavior. These reports can include, among others, the following:
- Audience reports: Audience reports help us get to know our users better and gain a more precise understanding of who is interested in our service.
- Advertising reports: Advertising reports make it easier for us to analyze and improve our online advertising.
- Acquisition reports: Acquisition reports provide helpful information on how we can attract more people to our service.
- Behavior reports: Here, we learn about how you interact with our website. We can track the path you take on our site and which links you click on.
- Conversion reports: Conversion refers to an action you take as a result of a marketing message, such as going from being a website visitor to becoming a buyer or newsletter subscriber. Through these reports, we gain insights into how our marketing efforts resonate with you, with the aim of improving our conversion rate.
- Real-time reports: With real-time reports, we can see what is currently happening on our website. For example, we can see how many users are currently reading this text.
In addition to the above-mentioned analysis reports, Google Analytics 4 also offers the following functions:
- Event-based data model: This model captures specific events that can occur on our website, such as playing a video, making a purchase, or subscribing to our newsletter.
- Advanced analytics features: With these features, we can gain a better understanding of your behavior on our website or certain general trends. For example, we can segment user groups, conduct comparative analyses of target audiences, or track your path on our website.
- Predictive modeling: Based on the collected data, missing data can be extrapolated through machine learning to predict future events and trends. This can help us develop better marketing strategies.
- Cross-platform analysis: Data collection and analysis are possible from both websites and apps. This enables us to analyze user behavior across platforms, provided you have consented to data processing.
Why do we use Google Analytics on our website?
Our goal with this website is clear: we want to provide you with the best possible service. The statistics and data from Google Analytics help us achieve this goal.
The statistically evaluated data gives us a clear picture of the strengths and weaknesses of our website. On one hand, we can optimize our site to make it more easily found by interested people on Google. On the other hand, the data helps us better understand you as a visitor. We know exactly what we need to improve on our website in order to provide you with the best possible service. The data also helps us conduct our advertising and marketing activities in a more personalized and cost-effective manner. After all, it only makes sense to show our products and services to people who are interested in them.
What data is stored by Google Analytics?
With the help of a tracking code, Google Analytics creates a random, unique ID associated with your browser cookie. This way, Google Analytics recognizes you as a new user, and a user ID is assigned to you. When you visit our site again, you are recognized as a “returning” user. All collected data is stored together with this user ID, making it possible to evaluate pseudonymous user profiles.
To analyze our website with Google Analytics, a property ID must be inserted into the tracking code. The data is then stored in the corresponding property. For each newly created property, the default is Google Analytics 4 Property. The data storage duration varies depending on the property used.
Through identifiers such as cookies, app instance IDs, user IDs, or custom event parameters, your interactions, if you have consented, are measured across platforms. Interactions encompass all types of actions you perform on our website. If you also use other Google systems (such as a Google account), data generated through Google Analytics can be linked to third-party cookies. Google does not disclose Google Analytics data unless we, as website operators, authorize it, except when required by law.
According to Google, IP addresses are not logged or stored in Google Analytics 4. However, IP address data is used by Google for deriving location data and is immediately deleted thereafter. All IP addresses collected from users in the EU are deleted before the data is stored in a data center or on a server.
Since GA4 focuses on event-based data, the tool uses significantly fewer cookies compared to previous versions such as Google Universal Analytics. However, there are still some specific cookies used by GA4. These can include:
Name: _ga
Value: 2.1326744211.152113238923-5
Purpose: By default, analytics.js uses the _ga cookie to store the user ID. It is used to distinguish website visitors.
Expiration: After 2 years
Name: _gid
Value: 2.1687193234.152113238923-1
Purpose: This cookie is also used to distinguish website visitors.
Expiration: After 24 hours
Name: gat_gtag_UA Value: 1
Purpose: Used to reduce the request rate. If Google Analytics is deployed via Google Tag Manager, this cookie will be named dc_gtm .
Expiration: After 1 minute
Note: This list cannot claim to be exhaustive, as Google may change their choice of cookies from time to time. GA4 aims to improve data privacy and offers several options for controlling data collection. For example, we can determine the storage duration ourselves and control data.
Here we provide an overview of the main types of data collected by Google Analytics:
Heatmaps: Google creates heatmaps to show the exact areas you click on. This provides us with information about your interactions on our site.
Session Duration: Google refers to session duration as the time you spend on our site without leaving. If you are inactive for 20 minutes, the session automatically ends.
Bounce Rate: Bounce rate refers to when you view only one page on our website and then leave.
Account Creation: If you create an account or place an order on our website, Google Analytics collects this data.
Location: IP addresses are not logged or stored in Google Analytics. However, location data is derived shortly before the IP address is deleted.
Technical Information: Technical information includes your browser type, internet service provider, and screen resolution, among others.
Source of Origin: Google Analytics is interested in the website or advertisement that brought you to our site.
Additional data may include contact information, reviews, media playback (e.g., if you play a video on our site), sharing of content via social media, or adding to favorites. This list is not exhaustive and serves only as a general guide to the data storage by Google Analytics.
Where and how long are the data stored?
Google has servers distributed worldwide. You can find precise information about the locations of Google data centers at:
https://datacenters.google/
Your data is distributed across multiple physical storage devices. This ensures faster access to data and better protection against manipulation. Each Google data center has emergency programs in place for your data. In the event of hardware failure or natural disasters, the risk of service interruption at Google remains low.
The retention period of data depends on the properties used. The storage duration is always set separately for each individual property. Google Analytics offers us four options for controlling the storage duration:
- 2 months: This is the shortest storage period.
- 14 months: By default, data is stored in GA4 for 14 months.
- 26 months: Data can also be stored for 26 months.
- Data is only deleted manually.
In addition, there is also the option for data to be deleted only if you do not visit our website within the selected time period. In this case, the retention period is reset every time you revisit our website within the defined time frame.
Once the defined period has expired, the data is deleted once a month. This retention period applies to data linked to cookies, user identification, and advertising IDs (e.g., cookies from the DoubleClick domain). Report results are based on aggregated data and are stored independently of user data. Aggregated data is a combination of individual data into larger units.
How can I delete my data or prevent data storage?
Under the data protection laws of the European Union, you have the right to access, update, delete, or restrict your data. By using the browser add-on to deactivate Google Analytics JavaScript (analytics.js, gtag.js), you can prevent Google Analytics 4 from using your data. You can download and install the browser add-on at:
https://tools.google.com/dlpage/gaoptout?hl=en Please note that this add-on only disables data collection by Google Analytics.
If you want to disable, delete, or manage cookies in general, you can find the respective instructions for the most common browsers in the “Cookies” section.
Legal basis
The use of Google Analytics requires your consent, which we obtained through our cookie popup. According to
Art. 6(1)(a) of the GDPR, this consent constitutes the legal basis for the processing of personal data that may occur during the collection by web analytics tools.
In addition to consent, we also have a legitimate interest in analyzing the behavior of website visitors to improve our offering technically and economically. By using Google Analytics, we can identify website errors, detect attacks, and improve efficiency. The legal basis for this is
Art. 6(1)(f) of the GDPR (legitimate interests). However, we only use Google Analytics if you have given your consent.
Google processes data from you, among other things, in the USA. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Google uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Google commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
You can find the Google Ads Data Processing Terms, which refer to the Standard Contractual Clauses, at:
https://business.safety.google/intl/en/adsprocessorterms/
We hope we have provided you with the most important information regarding the data processing by Google Analytics. If you want to learn more about the tracking service, we recommend the following links:
https://marketingplatform.google.com/about/analytics/terms/en/ and
https://support.google.com/analytics/answer/6004245?hl=en
If you want to learn more about data processing, you can refer to the Google Privacy Policy at:
https://policies.google.com/privacy?hl=en.
Google Analytics Reports on demographic characteristics and interests
We have turned on Google Analytics’ functions for advertising reports. These reports on demographic characteristics and interests contain details about age, gender and interests. Through them we can get a better picture of our users – without being able to allocate any data to individual persons. You can learn more about advertising functions at
auf https://support.google.com/analytics/answer/3450482?hl=en&%3Butm_id=ad.
You can terminate the use of your Google Account’s activities and information in “Ads Settings” at
https://adssettings.google.com/authenticated via a checkbox.
Google Analytics Google Signals Privacy Policy
We have activated Google signals in Google Analytics. Through this, any existing Google Analytics functions (advertising reports, remarketing, cross-device reports and reports on interests and demographic characteristics) are updated, to result in the summary and anonymisation of your data, should you have permitted personalised ads in your Google Account.
The special aspect of this is that it involves cross-device tracking. That means your data can be analysed across multiple devices. Through the activation of Google signals, data is collected and linked to the Google account. For example, it enables Google to recognise when you look at a product on a smartphone and later buy the product on a laptop. Due to activating Google signals, we can start cross-device remarketing campaigns, which would otherwise not be possible to this extent. Remarketing means, that we can show you our products and services across other websites as well.
Moreover, further visitor data such as location, search history, YouTube history and data about your actions on our website are collected in Google Analytics. As a result, we receive improved advertising reports and more useful information on your interests and demographic characteristics. These include your age, the language you speak, where you live or what your gender is. Certain social criteria such as your job, your marital status or your income are also included. All these characteristics help Google Analytics to define groups of persons or target audiences.
Those reports also help us to better assess your behaviour, as well as your wishes and interests. As a result, we can optimise and customise our products and services for you. By default, this data expires after 26 months. Please consider, that this data is only collected if you have agreed to personalised advertisement in your Google Account. The retained information is always exclusively summarised and anonymous data, and never any data on individual persons. You can manage or delete this data in your Google Account.
Google Analytics in Consent Mode
Depending on your consent, Google Analytics will progress your personal data in the so-called “consent mode”. You can choose whether or not you want to accept Google Analytics cookies, and thus which of your data Google Analytics may process. The retained data is mainly used to measure user behaviour on the website, to serve targeted advertising and to provide us with web analysis reports. Usually, you would consent to Google’s data processing via a cookie consent tool. If you do not consent to data processing, only aggregated data will be collected and processed. This means that data cannot be assigned to individual users and therefore no user profile will be created for you. You also have the option to only agree to statistical measurement, meaning that none of your personal data will be processed and used for advertising or advertising measurement sequences.
Google Analytics IP Anonymisation
We implemented Google Analytics’ IP address anonymisation to this website. Google developed this function, so this website can comply with the applicable privacy laws and the local data protection authorities’ recommendations, should they prohibit the retention of any full IP addresses.
The anonymisation or masking of IP addresses takes place, as soon as they reach Google Analytics’ data collection network, but before the data would be saved or processed.
You can find more information on IP anonymisation at
https://support.google.com/analytics/answer/2763052?hl=en.
| Google Remarketing Privacy Policy Summary
👥 Affected parties: Website visitors
🤝 Purpose: Economic success and optimization of our service performance.
📓 Processed data: Access statistics, including location data, device information, access duration and time, navigation behavior, and click behavior. Personal data such as IP addresses may also be processed.
📅 Storage duration: Conversion cookies usually expire after 30 days.
⚖️ Legal basis: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is Google Remarketing?
We use Google Remarketing as an online marketing measure to promote our products and services. Our goal is to make more people aware of the high quality of our offerings online. As part of our advertising measures, we use Google Remarketing provided by Google Inc. In Europe, the company responsible for all Google services is Google Ireland Limited (Gordon House, Barrow Street, Dublin 4, Ireland). This retargeting tool helps us better tailor and deliver our advertising to your interests and needs. In the following article, we will explain why we use Google Remarketing, what data is stored, and how you can prevent data storage.
Google Remarketing is a specialized online advertising method where targeted advertisements are displayed to users who have previously visited a specific website or app. This means that after visiting our website, the system recognizes which pages you viewed and your interests, enabling targeted online ads to be displayed based on this information. This works through the use of cookies and other tracking technologies that record your user behavior on our site and subsequently show relevant ads on other Google platforms (such as YouTube).
We are confident in the quality of our offerings and want as many people as possible to discover our website. In the online domain, Google Ads and its integrated Google Remarketing provide the best platform for this. Naturally, we also want a clear overview of the cost-effectiveness of our advertising campaigns, which is why we use Google Ads’ conversion tracking tool.
Why do we use Google Remarketing on our website?
We use Google Remarketing to highlight our offerings on other websites or Google platforms. The goal is to ensure our advertising campaigns reach only those genuinely interested in our offerings. With Google Remarketing, we can deliver targeted ads to you if you have previously visited our website and not completed a desired action. These ads aim to convince you that we have what you are looking for, thereby increasing the likelihood of further interaction or conversion. But what is a conversion? A conversion occurs when a purely interested website visitor becomes an acting visitor. This happens whenever you click on our ad and subsequently take another action, such as visiting our website.
This data helps us calculate our cost-effectiveness, measure the success of individual advertising efforts, and optimize our online marketing strategies. Additionally, the collected data allows us to make our website more engaging for you and customize our advertising offerings to your needs.
What data is stored by Google Remarketing?
We have integrated Google Remarketing into our website to analyze certain user actions better and display targeted ads. The data collected varies depending on the functions used and individual settings. Typically, information about which subpages you visit on our website, which products you view or purchase, how long you stay on a page, whether you abandon specific actions, or other conversions (purchase, button click, etc.) is collected.
As you can see, Google Remarketing primarily processes data related to your user behavior and does not process personal data such as names or email addresses. However, Google Remarketing processes your IP address, which is considered personal data under GDPR. Additionally, cookies or other tracking technologies may store information about your devices (browser, operating system, device type, etc.) and demographic data such as age or gender. All data is anonymized and aggregated to protect user privacy.
When you click on one of our Google Ads, the “Conversion” cookie is stored on your computer (usually in your browser) or mobile device. Cookies are small text files that store information on your computer.
Below are the details of the main cookies used for remarketing:
Name: Conversion
Value: EhMI_aySuoyv4gIVled3Ch0llweVGAEgt-mr6aXd7dYlSAGQ113238923-3
Purpose: This cookie stores every conversion you make on our site after arriving via a Google Ad.
Expiration: after 3 months
Name: _gac
Value: 1.1558695989.EAIaIQobChMIiOmEgYO04gIVj5AYCh2CBAPrEAAYASAAEgIYQfD_BwE
Purpose: This is a classic Google Analytics cookie used to record various actions on our website.
Expiration: after 3 months
Note: The _gac cookie appears only in conjunction with Google Analytics. The above list is not exhaustive, as Google regularly uses additional cookies for analytical purposes.
Once you complete an action on our website, Google recognizes the cookie and records your action as a conversion. As long as you browse our site and the cookie has not expired, we and Google can recognize that you returned to our site via a Google Ads ad. The cookie is read and the conversion data is sent back to Google Ads. Other cookies may also be used to measure conversions. Google Remarketing and the associated tracking can be further refined and enhanced with Google Analytics. For ads displayed by Google across the web, cookies named “__gads” or “_gac” may be set under our domain. Since September 2017, various campaign information from analytics.js has been stored in the _gac cookie. This cookie stores this data whenever you visit a page for which automatic tag labeling in Google Ads has been configured. Unlike cookies set for Google domains, Google can only read these conversion cookies while you are on our website.
How long and where is the data stored?
Google has servers distributed worldwide. You can read exactly where Google data centers are located here:
https://datacenters.google/
In general, Google processes data only as long as necessary to fulfill the purposes and as required by law. Please note that we have no control over how Google uses the data it collects. According to Google, data is encrypted and stored on secure servers. Most conversion cookies expire after 30 days and do not transmit personal data. The cookies named “Conversion” and “_gac” (used with Google Analytics) have an expiration date of 3 months.
How can I delete my data or prevent data storage?
You can opt out of Google Remarketing. By disabling Google Remarketing in your browser, you block tracking. In this case, you will not be included in the tool’s statistics. You can also change your browser’s cookie settings at any time. Each browser functions slightly differently. Under the “Cookies” section, you will find the corresponding links to the instructions for the most popular browsers.
If you generally do not want cookies, you can configure your browser to notify you whenever a cookie is set. This way, you can decide whether to allow or block each cookie. By downloading and installing this browser plug-in from
https://support.google.com/ads/answer/7395996, you can disable all “advertising cookies.” Please note that disabling these cookies does not prevent ads but only personalized advertising.
In your Google account settings, under “Ads” or “Advertising,” you can disable personalized ads based on Google Remarketing. If you do not consent to data processing through Google Remarketing via the consent management tool on our website, no data will be collected.
Legal Basis
If you have consented to the use of Google Remarketing, the legal basis for this data processing is your consent. According to
Art. 6 para. 1 lit. a GDPR (consent), this consent serves as the legal basis for processing personal data, such as the IP address collected through Google Remarketing.
We also have a legitimate interest in using Google Remarketing to optimize our online services and marketing measures. The corresponding legal basis for this is
Art. 6 para. 1 lit. f GDPR (legitimate interests). However, we only use Google Remarketing if you have given your consent.
Google processes your data, among other places, in the USA. Google is an active participant in the EU-US Data Privacy Framework, which ensures the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Google uses so-called Standard Contractual Clauses (= Art. 46 para. 2 and 3 GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission to ensure that your data complies with European data protection standards even when transferred to third countries (such as the USA) and stored there. Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Google commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an EU Commission implementation decision. You can find the decision and the corresponding Standard Contractual Clauses here:
https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
Google provides a data processing agreement under Art. 28 GDPR, which serves as the legal basis for our customer relationship with Google. This agreement refers to the EU Standard Contractual Clauses. Here you can find the data processing terms:
https://business.safety.google/intl/de/adsprocessorterms/.
Learn more about the data processed through the use of Google Remarketing in the privacy policy at
https://policies.google.com/privacy?hl=de.
Google Site Kit Privacy Policy
| Google Site Kit Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: Evaluation of visitor information to optimise the website.
📓 Processed data: Access statistics that contain data such as access location, device data, access duration and time, navigation behaviour, click behaviour and IP addresses. More details can be found below and in Google Analytics’ privacy policy.
📅 Storage period: depending on the properties used
⚖️ Legal bases: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is Google Site Kit?
We have integrated the WordPress plugin Google Site Kit of the American company Google Inc. to our website. For Europe, Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland) is responsible for all Google services. With Google Site Kit, we can quickly and easily view statistics of various Google products such as Google Analytics directly on our WordPress dashboard. The in Google Site Kit integrated tools also collect your personal data. In this privacy policy we will explain why we use Google Site Kit, how long and where your data is stored, and which other privacy policies may be relevant to you in this context.
Google Site Kit is a plugin for the WordPress content management system. With this plugin we can view important website analysis statistics directly in our dashboard. These are statistics that are collected by other Google products – primarily by Google Analytics. In addition to Google Analytics, the services Google Search Console, Page Speed Insight, Google AdSense, Google Optimize and Google Tag Manager can also be linked to Google Site Kit.
Why do we use Google Site Kit on our website?
As a service provider, it is our job to offer you the best possible experience on our website. You should feel comfortable on our website. Moreover, you should be able to quickly and easily find exactly what you are looking for. Statistical evaluations help us to get to know you better and to adapt our offer to your wishes and interests. We use various Google tools for these evaluations. Site Kit makes our work a lot easier because we can view and analyse the statistics of Google products on its dashboard. Therefore, we must no longer register for using the respective tools. Site Kit always provides a good overview of the most important analysis data.
What data are stored by Google Site Kit?
If you have consented to the use of tracking tools in the cookie notice (also called script or banner), cookies will be set by Google products such as Google Analytics. Also, on about you, such as your user behaviour, will be sent to Google, where it is stored and processed. This also includes personal data such as your IP address.
You can find more detailed information on the individual services in the respective separate sections of this privacy policy. In our privacy policy on Google Analytics for example, you will be able to view information on the exact types of data that are collected. You will also learn how long Google Analytics stores, manages and processes data, what cookies can be used and how you can prevent data retention. We also have respective comprehensive privacy policies for other Google services such as Google Tag Manager or Google AdSense.
In the following, we will show you exemplary Google Analytics cookies that may be set in your browser if you have consented to Google’s data processing. Please note that this list contains only a selection of potential cookies:
Name: _ga
Value:2.1326744211.152113238923-2
Purpose:Usually analytics.js uses the _ga cookie to store the user ID. Therefore, it can differentiate between website visitors.
Expiry date: after 2 years
Name: _gid
Value:2.1687193234.152113238923-7
Purpose: This cookie does also differentiate between website visitors.
Expiry date: after 24 hours
Name: _gat_gtag_UA_<property-id>
Value: 1
Purpose: This cookie is used to lower the request rate.
Expiry date: after 1 minute
How long and where are the data stored?
Google stores the collected data on its own servers, which are distributed all around the world. Most servers are in the United States, so your data may likely be stored there. At
https://datacenters.google/ you can see exactly where the company provides servers.
Data that is collected by Google Analytics is stored for a standard period of 26 months. After this time, your user data will be deleted. This retention period applies to any data linked to cookies, user identification and advertising IDs.
How can I delete my data or prevent data retention?
You always reserve the right to either receive information about your data, or to have your data deleted, rectified, or reduced. You can also deactivate, delete, or manage cookies in your browser at any time. In the following we will show you the respective instructions to do this in the most common browsers:
Chrome: Clear, enable and manage cookies in Chrome
Safari: Manage cookies and website data in Safari
Firefox: Clear cookies and site data in Firefox
Internet Explorer: Delete and manage cookies
Microsoft Edge: Delete cookies in Microsoft Edge
Please note that when using this tool, your data may also be stored and processed outside the EU. Under current European data protection law most third countries (including the USA) are not considered secure for this matter. Data must not be transferred to, stored and processed in such insecure third countries, unless there are suitable guarantees (such as EU standard contractual clauses) between us and the non-European service provider.
Legal basis
The use of Google Site Kit requires your consent, which we obtained via our cookie popup. According to
Art. 6 para. 1 lit. a GDPR (consent), this consent is the legal basis for processing personal data, such as when it is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors, and thus technically and economically improving our offer. With the help of Google Site Kit, we can recognise website errors, identify attacks and improve profitability. The legal basis for this is
Art. 6 para. 1 lit. f GDPR (legitimate interests). Nevertheless, we only use Google Site Kit if you have given us your consent.
Google processes data from you, among other things, in the USA. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Google uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Google commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
You can find the Google Ads Data Processing Terms, which refer to the Standard Contractual Clauses, at:
https://business.safety.google/intl/en/adsprocessorterms/
To find out more about data processing by Google, we recommend Google’s comprehensive privacy policy at
https://policies.google.com/privacy?hl=en-GB
Google Tag Manager Privacy Policy
| Google Tag Manager Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: Organisation of individual tracking tools
📓 Processed data: Google Tag Manager itself does not store any data. The data record tags of the web analytics tools used.
📅 Storage period: depending on the web analytics tool used
⚖️ Legal bases: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is Google Tag Manager?
We use Google Tag Manager by the company Google Inc. (1600 Amphitheatre Parkway Mountain View, CA 94043, USA) for our website.
This Tag Manager is one of Google’s many helpful marketing products. With it, we can centrally integrate and manage code sections of various tracking tools, that we use on our website.
In this privacy statement we will explain in more detail, what Google Tag Manager does, why we use it and to what extent your data is processed.
Google Tag Manager is an organising tool with which we can integrate and manage website tags centrally and via a user interface. Tags are little code sections which e.g. track your activities on our website. For this, segments of JavaScript code are integrated to our site’s source text. The tags often come from Google’s intern products, such as Google Ads or Google Analytics, but tags from other companies can also be integrated and managed via the manager. Since the tags have different tasks, they can collect browser data, feed marketing tools with data, embed buttons, set cookies and track users across several websites.
Why do we use Google Tag Manager for our website?
Everybody knows: Being organised is important! Of course, this also applies to maintenance of our website. In order to organise and design our website as well as possible for you and anyone who is interested in our products and services, we rely on various tracking tools, such as Google Analytics.
The collected data shows us what interests you most, which of our services we should improve, and which other persons we should also display our services to. Furthermore, for this tracking to work, we must implement relevant JavaScript Codes to our website. While we could theoretically integrate every code section of every tracking tool separately into our source text, this would take too much time and we would lose overview. This is the reason why we use Google Tag Manager. We can easily integrate the necessary scripts and manage them from one place. Additionally, Google Tag Manager’s user interface is easy to operate, and requires no programming skills. Therefore, we can easily keep order in our jungle of tags.
What data is stored by Google Tag Manager?
Tag Manager itself is a domain that neither uses cookies nor stores data. It merely functions as an “administrator“ of implemented tags. Data is collected by the individual tags of the different web analysis tools. Therefore, in Google Tag Manager the data is sent to the individual tracking tools and does not get saved.
However, with the integrated tags of different web analysis tools such as Google Analytics, this is quite different. Depending on the analysis tool used, various data on your internet behaviour is collected, stored and processed with the help of cookies. Please read our texts on data protection for more information on the articular analysis and tracking tools we use on our website.
We allowed Google via the account settings for the Tag Manager to receive anonymised data from us. However, this exclusively refers to the use of our Tag Manager and not to your data, which are saved via code sections. We allow Google and others, to receive selected data in anonymous form. Therefore, we agree to the anonymised transfer of our website data. However, even after extensive research we could not find out what summarised and anonymous data it is exactly that gets transmitted. What we do know is that Google deleted any info that could identify our website. Google combines the data with hundreds of other anonymous website data and creates user trends as part of benchmarking measures. Benchmarking is a process of comparing a company’s results with the ones of competitors. As a result, processes can be optimised based on the collected information.
How long and where is the data stored?
When Google stores data, this is done on Google’s own servers. These servers are located all over the world, with most of them being in America. At
https://datacenters.google/ you can read in detail where Google’s servers are.
In our individual data protection texts on the different tools you can find out how long the respective tracking tools store your data.
How can I delete my data or prevent data retention?
Google Tag Manager itself does not set any cookies but manages different tracking websites’ tags. In our data protection texts on the different tracking tools you can find detailed information on how you can delete or manage your data.
Please note that when using this tool, your data may also be stored and processed outside the EU. Most third countries (including the USA) are not considered secure under current European data protection law. Data must not be transferred, stored and processed to insecure third countries, unless there are suitable guarantees (such as EU standard contractual clauses) between us and the non-European service provider.
Legal basis
The use of the Google Tag Manager requires your consent, which we obtained via our cookie popup. According to
Art. 6 para. 1 lit. a GDPR (consent), this consent is the legal basis for personal data processing, such as when it is collected by web analytics tools.
In addition to consent, we have a legitimate interest in analysing the behaviour of website visitors and thus technically and economically improving our offer. With the help of Google Tag Managers we can also improve profitability. The legal basis for this is
Art. 6 para. 1 lit. f GDPR (legitimate interests). We only use Google Tag Manager if you have given us your consent.
Google processes data from you, among other things, in the USA. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Google uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Google commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
You can find the Google Ads Data Processing Terms, which refer to the Standard Contractual Clauses, at:
https://business.safety.google/intl/en/adsprocessorterms/
If you want to learn more about Google Tag Manager, we recommend their FAQs at
https://support.google.com/tagmanager/?hl=en#topic=3441530.
| Meta Conversions API Privacy Policy Summary
👥 Affected parties: Website visitors
🤝 Purpose: Optimization of our service performance
📓 Processed data: Data such as customer information, user behavior, device information, and your IP address.
More details can be found below in the privacy policy.
📅 Storage duration: Until the data is no longer useful for Meta’s purposes
⚖️ Legal basis: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What is the Meta Conversions API?
We use Meta Conversions API on our website, a server-side event tracking tool. The service provider is the American company Meta Platforms Inc. For the European region, the responsible company is Meta Platforms Ireland Limited (4 Grand Canal Square, Grand Canal Harbour, Dublin 2, Ireland).
The Meta Conversions API is a tool or function that can measure the performance of our advertising campaigns in real time. The API is an interface that connects our website with Meta and thus measures certain actions on our website. A conversion occurs when you, as a visitor to a website, perform a desired action. This can be, for example, clicking a button or filling out a registration form. This conversion tracking method is an alternative to the Meta Pixel and aims to optimize conversion tracking through precision and reliability. The API sends data directly from our server to Meta server-side. Personal data may also be processed in the process. In this privacy policy, we delve deeper into the data processing by us and Meta.
Why do we use the Meta Conversions API on our website?
We use the Meta Conversions API to improve the quality of our website, our offerings, and our advertising campaigns. Our goal is to provide you with the best possible service. We want you to feel comfortable on our website and get exactly what you expect. To achieve this, we need to tailor our offerings as closely as possible to your needs and preferences. The Meta Conversions API helps us adapt to this effectively and customize content and offers. This flexibility allows us to consider various needs while improving our online presence. The data also helps us conduct our advertising measures more economically and individually. We aim to present our offerings only to people who are genuinely interested in them.
What data is stored by the Meta Conversions API?
Using the Meta Conversions API, we can collect and provide Meta with various data on events occurring on our website. The specific data stored and processed depends on our individual settings and the specific events and parameters. Generally, event data, user data, device data, and the time at which an event (e.g., button click) occurred are recorded and sent to Meta. Event data includes actions such as registration, product purchase, page views, or button clicks on our website. User data may include personal information such as IP address, name, address, or email address. Device data refers to your device type, operating system, browser, and screen resolution.
How long and where is the data stored?
In general, Meta stores data until it is no longer needed for its own services and Meta products. Meta has servers distributed worldwide where data is stored. Customer data, however, is deleted within 48 hours after being matched with its user data.
How can I delete my data or prevent data storage?
You have the right and opportunity to access your personal data at any time and object to its use and processing. You can also file a complaint with a government supervisory authority at any time. You can generally prevent data storage by not consenting to data processing via the Consent Management Tool. Meta Conversions API operates server-side, making data deletion different from client-side methods. Nevertheless, you can review and adjust the privacy and security settings in your browser and, if possible, block tracking resources (pixels, cookies, scripts).
Legal Basis
If you have consented to your data being processed and stored by the Meta Conversions API, this consent serves as the legal basis for data processing
(Art. 6 para. 1 lit. a GDPR). Your data is also generally stored and processed based on our legitimate interest
(Art. 6 para. 1 lit. f GDPR) in effective and efficient communication with you or other customers and business partners. However, we only use the Meta Conversions API if you have given your consent.
Metaprocesses your data in the USA, among other places. Meta Platforms is an active participant in the EU-US Data Privacy Framework, which governs the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Meta also uses so-called Standard Contractual Clauses (= Art. 46 para. 2 and 3 GDPR). Standard Contractual Clauses (SCC) are templates provided by the EU Commission to ensure that your data also complies with European data protection standards when transferred to third countries (such as the USA) and stored there. Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Meta commits to complying with the European level of data protection when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an EU Commission implementation decision. You can find the decision and the corresponding Standard Contractual Clauses here:
https://eur-lex.europa.eu/eli/dec_impl/2021/914/oj?locale=de.
You can find Meta’s data processing terms, which refer to the Standard Contractual Clauses, at
https://www.facebook.com/legal/terms/dataprocessing.
Learn more about the data processed through the use of the Meta Conversions API in the privacy policy at
https://www.facebook.com/about/privacy.
We use Facebook’s Meta pixel on our website. For that, we have implemented a code on our website. The Meta pixel is a segment of a JavaScript code, which, in case you came to our website via Facebook ads, loads an array or functions that enable Facebook to track your user actions. For example, if you buy a product on our website, the Facebook pixel is triggered and stores your actions on our website in one or more cookies. These cookies enable Facebook to match your user data (customer data such as IP address, user ID) with the data of your Facebook account. After that, Facebook deletes your data again. The collected data is anonymous as well as inaccessible and can only be used for ad placement purposes. If you are a Facebook user and you are logged in, your visit to our website is automatically assigned to your Facebook user account.
We exclusively want to show our products or services to persons, who are interested in them. With the aid of the Meta pixel, our advertising measures can get better adjusted to your wishes and interests. Therefore, Facebook users get to see suitable advertisement (if they allowed personalised advertisement). Moreover, Facebook uses the collected data for analytical purposes and for its own advertisements.
In the following we will show you the cookies, which were set on a test page with the Meta pixel integrated to it. Please consider that these cookies are only examples. Depending on the interaction that is made on our website, different cookies are set.
Name: _fbp
Value: fb.1.1568287647279.257405483-6113238923-7
Purpose: Facebook uses this cookie to display advertising products.
Expiration date: after 3 months
Name: fr
Value: 0aPf312HOS5Pboo2r..Bdeiuf…1.0.Bdeiuf.
Purpose: This cookie is used for Meta pixels to function properly.
Expiration date: after 3 months
Name: comment_author_50ae8267e2bdf1253ec1a5769f48e062113238923-3
Value: Name of the author
Purpose: This cookie saves the text and name of a user who e.g. leaves a comment.
Expiration date: after 12 months
Name: comment_author_url_50ae8267e2bdf1253ec1a5769f48e062
Value: https%3A%2F%2Fwww.testseite…%2F (URL of the author)
Purpose: This cookie saved the URL of the website that the user types into a text box on our website.
Expiration date: after 12 months
Name: comment_author_email_50ae8267e2bdf1253ec1a5769f48e062
Value: email address of the author
Purpose: This cookie saves the email address of the user, if they provided it on the website.
Expiration date: after 12 months
Note: The above-mentioned cookies relate to an individual user behaviour. Moreover, especially concerning the usage of cookies, changes at Facebook can never be ruled out.
If you are registered on Facebook, you can change the settings for advertisements yourself at
https://www.facebook.com/ads/preferences/?entry_product=ad_settings_screen. If you are not a Facebook user, you can manage your user based online advertising at
https://www.youronlinechoices.com/uk/your-ad-choices. You have the option to activate or deactivate any providers there.
Facebook processes data from you, among other things, in the USA. Facebook respectively Meta Platforms is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Facebook uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Facebook commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
The Facebook Data Processing Term, which references the Standard Contractual Clauses, can be found at
https://www.facebook.com/legal/terms/dataprocessing.
If you want to learn more about Facebook’s data protection, we recommend you the view the company’s in-house data policies at
https://www.facebook.com/policy.php.
Privacy Policy for Facebook‘s Automatic Advanced Matching
Along with Facebook’s pixel function, we have also activated Automatic Advanced Matching. This function allows us to send hashed emails, names, genders, cities, states, postcodes and dates of birth or telephone numbers as additional information to Facebook, provided you have made them available to us. This activation gives us the opportunity to customise advertising campaigns even better to persons who are interested in our services or products.
Web Design Introduction
| Web Design Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: improvement of user experience
📓 Processed data: depends heavily on the services used. Usually, data such as IP address, technical data, language settings, browser version, screen resolution and browser name are processed. You can find more details directly with the respective web design tools.
📅 Storage duration: depends on the tools used
⚖️ Legal bases: Article 6 paragraph 1 lit. a GDPR (consent), Article 6 paragraph 1 lit. f GDPR (legitimate interests) |
What is web design?
We use various tools on our website for the purpose of our web design. Contrary to common belief, web design is not just about making our website look nice, but rather also about functionality and performance. But of course, a good-looking website is also a major goal of professional web design. Web design is a part of media design and deals with the visual as well as the structural and functional design of a website. Our aim with our web design is to improve your experience on our site. In web design jargon, this is called User Experience (UX) and usability. User Experience entails all impressions and experiences that website visitors come across on a website. What is more, usability is part of the User Experience, as it determines how user-friendly a website is. This includes the clear structuring of content, subpages or products, along with how quickly and easily the website enables you to find what you are looking for. In order to offer you the best possible experience on our website, we also use so-called third-party web design tools. Therefore, all tools and services that help improve our website’s design are classified under the category “web design”. This may, for example, include fonts, various plugins or other integrated web design functions.
Why do we use web design tools?
The way you absorb information on a website depends very much on its structure, functionality and visual perception. Therefore, good and professional web design has become increasingly important for us. We are constantly working on improving our site as a way of further extending our services for you as a website visitor. Furthermore, a beautiful and functioning website also has economic advantages for us. Needless to say, you will only visit it and take advantage of our offers if you feel completely at ease.
What data is stored by web design tools?
When you visit our website, any web design elements integrated into our pages may process your data. The exact data that is processed depends on the tools used. Below you can see exactly which tools we use for our website. For more information about data processing, we recommend you also read the respective privacy policy of the respective tools. There you can usually find out which data is processed, whether cookies are used and how long the data is stored. Moreover, fonts such as Google Fonts, for example, also automatically transmit information such as your language settings, IP address, browser version, browser screen resolution and browser name to Google’s servers.
Duration of data processing
Data processing times are very individual and depend on the web design elements used. For example, when cookies are used, the retention period can be as little as a minute, but it may also be a few years. Please make yourself familiar with this topic. You may for example read our general section on cookies as well as the Privacy Policies of the tools used. There you can likely find out exactly which cookies are used and what information is stored there. For example, Google Font files are stored for one year, in order to improve the loading speed of a website. In principle, data is only kept for as long as is necessary to provide the service. But legal requirements may require data to be stored for longer.
Right to object
You also retain the right and the option to revoke your consent to the use of cookies or third-party providers at any time. You can do this either via our cookie management tool or via other opt-out functions. You can also prevent cookies from collecting your data by managing, deactivating or deleting the cookies in your browser. However, among web design elements (typically fonts) there is also data that cannot be erased easily. This is the case whenever data is automatically collected as soon as a page is accessed and then directly transmitted to a third party (e.g. Google). In these cases, please contact the support of the respective provider. In the case of Google, you can reach support at
https://support.google.com/?hl=de.
Legal Basis
If you have consented to the use of web design tools, this consent serves as the legal basis for the relevant data processing. According to Article 6 (1) (a) GDPR (consent), your consent represents the legal basis for the processing of personal data, as it may occur when it is collected by web design tools. We also have a legitimate interest in web design to improve on our website. After all, only then can we provide you with a beautiful and professional web offer. The corresponding legal basis for this is Article 6 (1) (f) GDPR (legitimate interests). However, we strongly want to emphasise once more that we only use web design tools if you have given your consent.
You can find information on different web design tools – if available – in the following sections.
Adobe Fonts Privacy Policy
We use Adobe’s Typekit fonts on our website, which is a web font hosting service. The provider of this service is the American company Adobe Inc. The Irish company Adobe Systems Software Ireland Companies, 4-6 Riverwalk, Citywest Business Campus, Dublin 24, Ireland, is responsible for the European region.
Adobe processes data from you, among other things, in the USA. Adobe is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Adobe uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Adobe commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
You can find out more about the standard contractual clauses at Adobe at
https://www.adobe.com/uk/privacy/eudatatransfers.html.
You can find out more about the data processed by using Adobe Fonts in the Privacy Policy at
https://www.adobe.com/de/privacy.html.
Google Fonts Privacy Policy
| Google Fonts Privacy Policy Overview
👥 Affected parties: website visitors
🤝 Purpose: service optimisation
📓 Processed data: data such as IP address, CSS and font requests
You can find more details on this in the Privacy Policy below.
📅 Storage period: Google stores font files for one year
⚖️ Legal bases: Art. 6 para. 1 lit. a GDPR (consent), Art. 6 para. 1 lit. f GDPR (legitimate interests) |
What are Google Fonts?
On our website we use Google Fonts, by the company Google Inc. (1600 Amphitheatre Parkway Mountain View, CA 94043, USA).
To use Google Fonts, you must log in and set up a password. Furthermore, no cookies will be saved in your browser. The data (CSS, Fonts) will be requested via the Google domains fonts.googleapis.com and fonts.gstatic.com. According to Google, all requests for CSS and fonts are fully separated from any other Google services. If you have a Google account, you do not need to worry that your Google account details are transmitted to Google while you use Google Fonts. Google records the use of CSS (Cascading Style Sheets) as well as the utilised fonts and stores these data securely. We will have a detailed look at how exactly the data storage works.
Google Fonts (previously Google Web Fonts) is a directory with over 800 fonts that
Google provides its users free of charge.
Many of these fonts have been published under the SIL Open Font License license, while others have been published under the Apache license. Both are free software licenses.
Why do we use Google Fonts on our website?
With Google Fonts we can use different fonts on our website and do not have to upload them to our own server. Google Fonts is an important element which helps to keep the quality of our website high. All Google fonts are automatically optimised for the web, which saves data volume and is an advantage especially for the use of mobile terminal devices. When you use our website, the low data size provides fast loading times. Moreover, Google Fonts are secure Web Fonts. Various image synthesis systems (rendering) can lead to errors in different browsers, operating systems and mobile terminal devices. These errors could optically distort parts of texts or entire websites. Due to the fast Content Delivery Network (CDN) there are no cross-platform issues with Google Fonts. All common browsers (Google Chrome, Mozilla Firefox, Apple Safari, Opera) are supported by Google Fonts, and it reliably operates on most modern mobile operating systems, including Android 2.2+ and iOS 4.2+ (iPhone, iPad, iPod). We also use Google Fonts for presenting our entire online service as pleasantly and as uniformly as possible.
Which data is stored by Google?
Whenever you visit our website, the fonts are reloaded by a Google server. Through this external cue, data gets transferred to Google’s servers. Therefore, this makes Google recognise that you (or your IP-address) is visiting our website. The Google Fonts API was developed to reduce the usage, storage and gathering of end user data to the minimum needed for the proper depiction of fonts. What is more, API stands for „Application Programming Interface“ and works as a software data intermediary.
Google Fonts stores CSS and font requests safely with Google, and therefore it is protected. Using its collected usage figures, Google can determine how popular the individual fonts are. Google publishes the results on internal analysis pages, such as Google Analytics. Moreover, Google also utilises data of ist own web crawler, in order to determine which websites are using Google fonts. This data is published in Google Fonts’ BigQuery database. Enterpreneurs and developers use Google’s webservice BigQuery to be able to inspect and move big volumes of data.
One more thing that should be considered, is that every request for Google Fonts automatically transmits information such as language preferences, IP address, browser version, as well as the browser’s screen resolution and name to Google’s servers. It cannot be clearly identified if this data is saved, as Google has not directly declared it.
How long and where is the data stored?
Google saves requests for CSS assets for one day in a tag on their servers, which are primarily located outside of the EU. This makes it possible for us to use the fonts by means of a Google stylesheet. With the help of a stylesheet, e.g. designs or fonts of a website can get changed swiftly and easily.
Any font related data is stored with Google for one year. This is because Google’s aim is to fundamentally boost websites’ loading times. With millions of websites referring to the same fonts, they are buffered after the first visit and instantly reappear on any other websites that are visited thereafter. Sometimes Google updates font files to either reduce the data sizes, increase the language coverage or to improve the design.
How can I erase my data or prevent it being stored?
The data Google stores for either a day or a year cannot be deleted easily. Upon opening the page this data is automatically transmitted to Google. In order to clear the data ahead of time, you have to contact Google’s support at
https://support.google.com/?hl=en-GB&tid=113238923. The only way for you to prevent the retention of your data is by not visiting our website.
Unlike other web fonts, Google offers us unrestricted access to all its fonts. Thus, we have a vast sea of font types at our disposal, which helps us to get the most out of our website. You can find out more answers and information on Google Fonts at
https://developers.google.com/fonts/faq?tid=113238923. While Google does address relevant elements on data protection at this link, it does not contain any detailed information on data retention.
It proofs rather difficult to receive any precise information on stored data by Google.
Legal basis
If you have consented to the use of Google Fonts, your consent is the legal basis for the corresponding data processing. According to
Art. 6 Paragraph 1 lit. a GDPR (Consent) your consent is the legal basis for the processing of personal data, as can occur when it is processed by Google Fonts.
We also have a legitimate interest in using Google Font to optimise our online service. The corresponding legal basis for this is
Art. 6 para. 1 lit. f GDPR (legitimate interests). Nevertheless, we only use Google Font if you have given your consent to it.
Google processes data from you, among other things, in the USA. Google is an active participant in the EU-US Data Privacy Framework, which regulates the correct and secure transfer of personal data from EU citizens to the USA. More information can be found at
https://commission.europa.eu/document/fa09cbad-dd7d-4684-ae60-be03fcb0fddf_en.
Additionally, Google uses so-called Standard Contractual Clauses (Article 46(2) and (3) GDPR). Standard Contractual Clauses (SCC) are template clauses provided by the EU Commission and are designed to ensure that your data complies with European data protection standards, even when transferred and stored in third countries (such as the USA). Through the EU-US Data Privacy Framework and the Standard Contractual Clauses, Google commits to maintaining the European data protection level when processing your relevant data, even if the data is stored, processed, and managed in the USA. These clauses are based on an implementing decision of the EU Commission. You can find the decision and the corresponding Standard Contractual Clauses here:
https://ec.europa.eu/commission/presscorner/detail/en/ip_21_2847.
You can find the Google Ads Data Processing Terms, which refer to the Standard Contractual Clauses, at:
https://business.safety.google/intl/en/adsprocessorterms/
You can find more information on which data is generally retained by Google and what this data is used at
https://policies.google.com/privacy?hl=en-GB.
Google Fonts Local Privacy Policy
On our website we use Google Fonts, by the company Google Inc. The responsible entity for the European area is Google Ireland Limited (Gordon House, Barrow Street Dublin 4, Ireland). We have integrated Google fonts locally, i.e. on our web server and not on Google’s servers. This means that no connection to Google’s servers and therefore no data transfer or retention take place.
What are Google Fonts?
Google Fonts was previously called Google Web Fonts. It is an interactive list with over 800 fonts which
Google offer for free use. With the use of Google Fonts, it is possible to utilise fonts without uploading them to your own server. In order to prevent any transfer of information to Google’s servers, we downloaded the fonts to our own server. This way we can comply with data privacy and do not transmit any data to Google Fonts.
Explanation of the terminology used
We always strive to make our privacy policy as clear and comprehensible as possible. However, this is not always easy, especially when it comes to technical and legal matters. It is often sensible to use legal terms (such as ‘personal data)’ or certain technical terms (such as ‘cookies’ or ‘IP address’). But we don’t want to use such terms without any explanation. This is why you will find an alphabetical list of important terms used below. These are terms we may not yet have sufficiently explained in the privacy policy. In case we have adopted any of these terms from the GDPR which are definitions, we will also list the GDPR texts here and add our own further explanations if necessary.
Processor
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“processor” means a natural or legal person, public authority, agency or other body which processes personal data on behalf of the controller;
Explanation: As a company and a website owner, we are responsible for all your data we process (i. e. the ‘controller’). In addition to the controller, there may also be so-called processors. This includes any company or person who processes personal data on our behalf. In addition to service providers such as tax consultants, processors can also be hosting or cloud providers, payment or newsletter providers or large companies such as Google or Microsoft.
Consent
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“consent” of the data subject means any freely given, specific, informed and unambiguous indication of the data subject’s wishes by which he or she, by a statement or by a clear affirmative action, signifies agreement to the processing of personal data relating to him or her;
Explanation: With websites, such consent is usually given via a cookie consent tool. You’ve most certainly come across these. Whenever you visit a website for the first time, you will usually be asked via a banner whether you agree or consent to the data processing. You can usually also make individual settings and thus decide for yourself which level of data processing you want to allow. If you do not give your consent, no personal data may be processed. Consent can of course also be given in writing, i.e. not via a tool.
Data concerning health
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“Data concerning health” means personal data related to the physical or mental health of a natural person, including the provision of health care services, which reveal information about his or her health status;
Explanation: Health data includes all stored information relating to your own health. It is often data that is also noted in patient files. This includes, for example, which medication you are using, X-rays, your entire medical history or your vaccination statuses.
Personal Data
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“personenal data” means any information relating to an identified or identifiable natural person (‘data subject’); an identifiable natural person is one who can be identified, directly or indirectly, in particular by reference to an identifier such as a name, an identification number, location data, an online identifier or to one or more factors specific to the physical, physiological, genetic, mental, economic, cultural or social identity of that natural person;
Explanation: Personal data is all data that can identify you as a person. This is usually data such as:
- name
- address
- email address
- postal address
- phone number
- birthday
- identification numbers such as social security number, tax identification number, ID card number or matriculation number
- banking data such as account number, credit information, account balances and more.
According to the European Court of Justice (ECJ), your
IP address is also personal data. IT experts can use your IP address to determine at least the approximate location of your device and subsequently your location as the connection owner. Therefore, storing an IP address also requires a legal basis within the scope of the GDPR. There are also so-called
“special categories” of personal data, which are particularly worthy of protection. These include:
- racial and ethnic origin
- political opinions
- religious or ideological beliefs
- Union membership
- genetic data such as data obtained from blood or saliva samples
- biometric data (this is information about psychological, physical or behavioural characteristics that can identify an individual).
health Data
- Data relating to sexual orientation or sex life
Profiling
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“Profiling” means any form of automated processing of personal data consisting of the use of personal data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that natural person’s performance at work, economic situation, health, personal preferences, interests, reliability, behaviour, location or movements;
Explanation: Profiling collects various personal data about an individual in order to learn more about that individual. On the internet, profiling is often used for advertising purposes or for credit checks. Web and advertising analysis programs e. g. collect data about your behaviour and interests on a website. This results in a special user profile that can be used to target advertising to specific target groups.
Controller
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“controller” means the natural or legal person, public authority, agency or other body which, alone or jointly with others, determines the purposes and means of the processing of personal data; where the purposes and means of such processing are determined by Union or Member State law, the controller or the specific criteria for its nomination may be provided for by Union or Member State law;
Explanation: In our example, we are responsible for the processing of your personal data and are therefore the “controller”. If we pass on collected data to other service providers for processing, they are considered “contract processors”. For this, a “Data Processing Agreement (DPA)” must be concluded.
Processing
Definition according to Article 4 of the GDPR
For the purposes of this Regulation, the term means:
“processing” means any operation or set of operations which is performed on personal data or on sets of personal data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination or otherwise making available, alignment or combination, restriction, erasure or destruction;
Note: When we talk about processing in our Privacy Policy, we talk about any type of data processing. As mentioned above in the original GDPR declaration, this includes not only the collection but also the storage and processing of data.
All texts are copyrighted.